
Posts Tagged ‘authentication-bypass’
JFrog Artifactory Authentication Bypass Exploited
A JFrog Artifactory authentication bypass is now under active exploitation: attackers are minting themselves unauthenticated administrator tokens on self-hosted Artifactory instances just days after JFrog disclosed the flaw. Tracked as CVE-2026-82329 (CVSS 9.8), the bug sits in Artifactory’s default, out-of-the-box configuration — no misconfiguration required, no credentials needed. What Happened JFrog disclosed the JFrog Artifactory…
Read MoreExchange Authentication Bypass Vulnerability Now Exploitable
A working exploit for an Exchange authentication bypass vulnerability is now public on GitHub, and heise.de reports that roughly 85% of on-premises Exchange servers in Germany remain vulnerable three weeks after Microsoft shipped a fix. The catch: for organizations still running Exchange 2016 or 2019, that fix is locked behind Microsoft’s paid Extended Security Update…
Read MoreminiOrange SAML SSO Bypass Vulnerability
A miniOrange SAML SSO bypass is under active exploitation against WordPress sites, and most vulnerability scanners cannot detect whether a given site is actually affected. Two chained authentication bugs, CVE-2026-61979 and CVE-2026-15981 (CVSS 9.8 each), let an unauthenticated attacker forge a SAML login and access wp-admin as any existing user, including administrators. DigitalOcean confirmed exploitation…
Read MoreCheck Point SmartConsole CVE-2026-16232: Admin Bypass

Check Point SmartConsole CVE-2026-16232 is now on CISA’s Known Exploited Vulnerabilities list: an unauthenticated attacker can forge a login token and get full administrator access to the console that manages an organization’s entire firewall fleet. Check Point patched it on July 22 and confirmed a handful of customers were already targeted. The federal remediation deadline…
Read MoreGitea Docker CVE-2026-20896 Auth Bypass
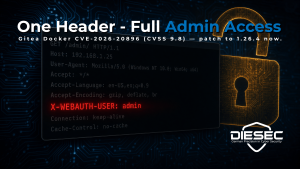
Gitea Docker CVE-2026-20896 is now under active exploitation: a single crafted HTTP header lets an unauthenticated attacker impersonate any user of a self-hosted Gitea instance — including an administrator — and walk away with private repositories and any secrets committed by mistake. What Happened Gitea’s official Docker image ships with REVERSE_PROXY_TRUSTED_PROXIES=*. On deployments that also…
Read More