
Supply Chain Security
GUTcert critical infrastructure data breach
A GUTcert critical infrastructure data breach has exposed roughly 640 GB of documentation submitted by German energy-grid operators as certification evidence, including exact substation locations and network topology maps. On September 24, Darmstadt utility ENTEGA AG confirmed it is a downstream victim, and more operators are expected to come forward. What Happened GUTcert is a…
Read MoreKeyv npm Supply Chain Attack Hits 2 Billion Installs
The Keyv npm supply chain attack compromised a single GitHub maintainer account and used it to push a credential-stealing worm into hundreds of widely used caching packages. By August 5, trackers put the count at 868 packages and 1,381 versions, spanning a combined 2 billion-plus monthly installs — the largest software supply-chain incident DIESEC has…
Read MoreAsyncAPI npm Supply Chain Attack: No Token Stolen
The AsyncAPI npm supply chain attack shows that neither of the two controls teams were told to trust — cryptographic provenance and blocking install scripts — actually stopped it: an attacker published four trojanized packages with valid SLSA/OIDC provenance attestations, without ever stealing an npm token, and the payload runs regardless of –ignore-scripts. What Happened…
Read MorePolinRider Supply Chain Attack Hits 108 Packages
The PolinRider supply chain attack has been confirmed by Socket.dev, SecurityWeek and SC Media: a North Korea-linked actor has flooded four separate open-source ecosystems — npm, Packagist, Go modules and the Chrome Web Store — with 108 malicious packages designed to steal developer and cloud credentials. What Happened Researchers attribute the PolinRider supply chain attack…
Read MoreKlue OAuth Breach — One Legacy Credential, Nine Security Vendors Compromised
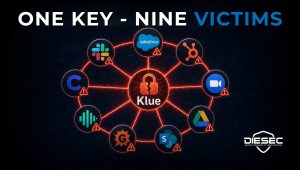
The security vendor you trust just got hacked — and took nine of its customers with it. The Icarus extortion group compromised Klue, a competitive intelligence platform. They didn’t need a zero-day. They found a single legacy credential, got into Klue’s backend, and pushed a code update that silently harvested OAuth tokens for every active…
Read More