
Cyber Dependencies and Attack Surface: ENISA 2026
The ENISA Threat Landscape 2026, published on 22 September, has a message that gets less attention than the usual list of threats: organisations are increasingly exposed through their cyber dependencies, meaning the technologies, suppliers and services they rely on. For German businesses, that means cyber risk no longer sits only in internal networks and endpoints. It also sits in cloud platforms, software suppliers, remote support channels, managed providers and the operational systems that keep services running.
A compromised external relationship can allow an attacker to affect more than one organisation, particularly when the relationship provides shared access or supports a widely used service. You can invest in endpoint security, awareness training and identity protection and still be disrupted through a supplier account, a shared platform, a software dependency or a forgotten management interface. So the question for 2026 is less which threats are most common and more which cyber dependencies give attackers the most reach.
ENISA 2026 looks at how connected systems spread the impact of an attack.
What ENISA 2026 Actually Says
ENISA’s headline findings include the familiar ones. Ransomware remains the most impactful short-term threat, geopolitics keeps shaping hacktivist activity, and AI is expected to play a bigger part in malicious operations. The framing has shifted, though. In its announcement, ENISA says cyber dependencies expand the attack surface and call for a new level of vigilance to prevent and mitigate incidents.
ENISA reports that attacks on cyber dependencies, including supply-chain and third-party attacks, continued during the reporting period. Attackers use interconnection to scale: compromise one provider, repository or platform and the effects reach many organisations downstream. The report’s own example is a ransomware attack on a Swedish IT supplier that affected about 200 municipalities and regional authorities.
The numbers point the same way. According to the report, essential and important entities under NIS2 accounted for 73 percent of recorded events. Public administration was the most targeted sector at 31.8 percent, followed by business services (8.5 percent), transport (8 percent), manufacturing (6.9 percent) and finance and banking (5.6 percent). ENISA also reports that ideology-driven DDoS activity accounted for 81.8 percent of the incidents recorded in public administration, so the sector ranking measures incident volume rather than business impact. The NIS2 figure matters more here: most recorded events involved organisations that already fall under the strictest governance and resilience requirements.
One compromised provider can give attackers a route into many customers.
Why Cyber Dependencies Matter More Now
Most organisations have spent years hardening email, endpoints, identity systems and remote work. Those investments still matter, but they do not cover the wider trust environment a modern business runs in. Many companies now rely on SaaS tools, open-source components, outsourced monitoring, software updates, API integrations, remote maintenance channels and specialist operational technology vendors.
Each of those relationships saves effort, and each concentrates risk. A managed service provider with administrative access across many customers is an efficient way into several of them at once. A software component embedded in many products can create a broad remediation effort, including for organisations that had no direct relationship with the original supplier.
In 2026, “attack surface” needs a wider reading. It is more than the list of internet-facing assets you know about. It includes every trusted relationship that can grant data access, privilege escalation, administrative control, software distribution or the power to interrupt a service. Securing known internet-facing assets does not by itself address the risks created by trusted third-party access, shared platforms or software dependencies.
Many German sectors rely on the same kinds of shared platforms and providers.
The German Business Context
Germany’s NIS2 implementation entered into force in December 2025 through changes to the BSI Act. Legal and compliance analyses broadly agree that it expands obligations around risk management, incident reporting and management responsibility. Management bodies of in-scope organisations are expected to approve and oversee cybersecurity risk-management measures, and commentary on the revised act stresses board-level accountability and potential personal consequences under the applicable legal framework. What that means for your company in particular is a question for your legal adviser.
For security teams, third-party access, software supply-chain exposure and remote operational dependencies stop being technical side notes once they can affect resilience, reporting duties or regulatory scrutiny.
Germany’s economic structure adds to the exposure. Manufacturing, logistics, healthcare, public administration, utilities, retail and business services all depend on specialist providers, integrated platforms and distributed operational systems. A supplier-linked incident can hit production, transport, customer delivery, environmental controls or regulated services, even when your own security baseline looks sound on paper.
The dependencies nobody has mapped are the ones nobody is watching.
Common Cyber Dependency Blind Spots
Incomplete mapping
Many organisations can name their main vendors. Far fewer can say quickly which suppliers hold administrative access, which systems rely on third-party APIs, which business processes depend on one platform, or which remote support channels could be abused during an incident. Without that overview, critical dependencies get discovered after something has gone wrong.
Too much faith in paperwork
Certifications, security questionnaires and contracts are useful signals. They do not show that access is tightly controlled, that logging is adequate, that emergency revocation works or that segmentation limits the damage. Until those controls have been tested, the paperwork only suggests maturity.
A gap between IT and operational security
Dependency risk does not stop at cloud platforms and office software. It reaches building-management systems, environmental controls and industrial processes. The recent attack affecting French supermarket refrigeration is a useful illustration. As of writing, reports say several retail groups were affected overnight from 11 to 12 October, that stores had to throw away stock, and that the Paris prosecutor’s office has opened an investigation. The incident is still developing, and details such as the number of affected stores and the technical route used by the attackers have not been fully established and may change. It still shows how quickly a digital route into operational systems can turn into physical and commercial damage.
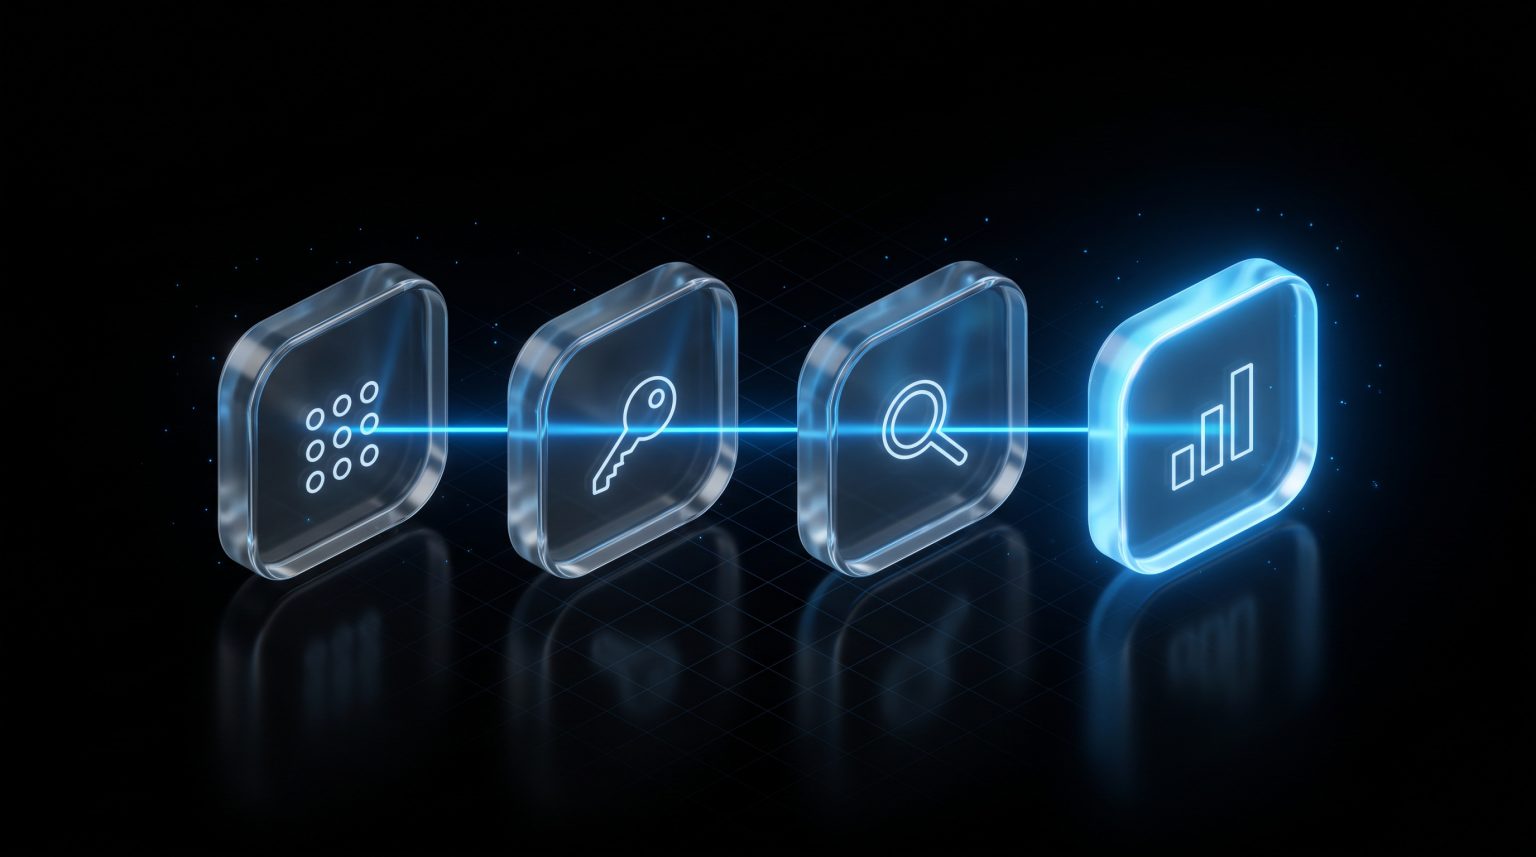
Four practical steps: map, govern access, validate, report.
What Organisations Should Do Now
First, identify the dependencies that matter to critical services. Not every supplier needs the same depth of review, but you should know which external relationships can affect identity, remote administration, software delivery, customer data, regulated reporting, safety or operational continuity. The inventory should list access methods, business owners, recovery responsibilities and technical choke points, not only names and contracts.
Second, reduce and govern remote access. Keep third-party administrative accounts to a minimum, protect them with strong authentication, log them, review them regularly and give each one an internal owner instead of leaving it to the vendor. Where supplier access is essential, define and test how you would suspend it quickly, preserve evidence and keep operating if you suspect a compromise.
Third, validate beyond self-assessment. Penetration testing finds exposed interfaces and weak trust assumptions, adversary simulation shows whether a foothold through a supplier could lead to real business impact, and tabletop exercises make teams work through incident-response decisions that involve outsourced or shared systems. You cannot remove dependencies, so the aim is to limit them, keep them visible and make sure they hold up under stress.
Fourth, make management reporting practical. Executives do not need a long vendor list with generic risk labels. They need answers to a handful of questions: which dependencies are critical, which could cause systemic disruption, how fast remote access can be cut, which reporting obligations would be triggered, and where compensating controls are still weak.
Known and governed dependencies make the attack surface easier to manage.
Closing Thoughts
ENISA 2026 explains why incidents cross organisational boundaries and why defending your own assets is not enough. Attackers want leverage as much as access, and a dependency provides it when one compromise connects to many environments, customers or processes.
For German businesses, that ties ENISA’s analysis to NIS2 governance duties, supply-chain scrutiny and operational resilience, and it forces a decision about which trust relationships to look at first. Organisations that map their dependencies, cut implicit trust and test privileged pathways will be better placed than those that still file third-party exposure under procurement. DIESEC’s penetration testing can help you check which of those pathways an attacker could actually use.
Sources (ENISA): ENISA Threat Landscape, ENISA: Exploring the evolution of the cyber threat landscape, ENISA Threat Landscape 2026 (PDF). Legal and compliance commentary (secondary sources): Greenberg Traurig: NIS2 in Germany, OpenKRITIS: NIS2 in Germany, NISD2 wiki: NIS2 in Germany.
Dependency reviews work best when security, IT and operations sit at one table.
