
Daily News
Three CVSS 10.0 Vulnerabilities in Ubiquiti UniFi OS — Zero Auth, Full Network Control
Three CVSS 10.0 vulnerabilities in Ubiquiti UniFi OS. One exploit chain. Full network control. Zero authentication required. If you use UniFi in your office — and most DACH SMBs do — this is your highest-priority patch this week. CISA added three Ubiquiti vulnerabilities to its Known Exploited Vulnerabilities catalog on June 23, confirming active exploitation…
Read MoreAI Agent Finds 21 FFmpeg Zero-Days for $1,000 — Chrome 149 Patches Record 429 Bugs
An AI agent just did what would take a skilled security researcher months — and it cost $1,000. Security startup depthfirst ran an autonomous AI agent against FFmpeg, the media processing library embedded in virtually every video call platform, streaming service, and recording tool. The agent scanned 1.5 million lines of C code and found…
Read MoreKlue OAuth Breach — One Legacy Credential, Nine Security Vendors Compromised
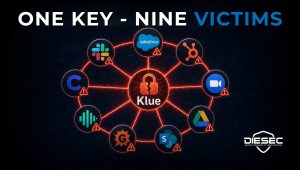
The security vendor you trust just got hacked — and took nine of its customers with it. The Icarus extortion group compromised Klue, a competitive intelligence platform. They didn’t need a zero-day. They found a single legacy credential, got into Klue’s backend, and pushed a code update that silently harvested OAuth tokens for every active…
Read MoreDragonForce Ransomware Hides C2 Traffic Inside Microsoft Teams Relay Servers
Ransomware operators found a backdoor into your network. It looks exactly like a Teams meeting. Symantec and Carbon Black disclosed that DragonForce ransomware affiliates deployed Backdoor.Turn — a Go-based implant that tunnels its command-and-control traffic through Microsoft Teams TURN relay servers. The malware obtains an anonymous Teams visitor token, uses a legitimate Microsoft relay for…
Read MoreAttackers just got admin access to the system that was supposed to catch them.
Attackers just got admin access to the system that was supposed to catch them. Splunk Enterprise has a CVSS 9.8 vulnerability — CVE-2026-20253 — that allows unauthenticated remote attackers to write arbitrary files on the Splunk server without any credentials. File write chains into full remote code execution. CISA confirmed active exploitation yesterday and added…
Read More